

Salesforce Authenticator analysis by Appwee
When I use a business account from a phone, the password is rarely the part that worries me most. The bigger concern is what happens if that password is guessed, reused, or exposed somewhere else. Salesforce Authenticator is built around one focused answer: adding a second verification step before access is completed. I find that narrow purpose useful because it turns account security into a quick decision on the phone instead of asking me to trust a password alone.
This is a free business app from Salesforce.com, inc., available for Everyone and listed for devices running iOS 9 or later. It has been around since November 4, 2013, and the current version is 4.8.0. Its popularity is also easy to understand: the app has passed five million installs, with an average rating of 4.4 from roughly twenty-seven thousand ratings. Those figures do not make it automatically right for every person, but they do show that it is being used as a practical security companion rather than as a niche experiment.
Why the second verification step matters
The main capability is two-step verification. In simple terms, signing in requires more than the password typed on the website or service. The phone becomes an additional checkpoint, helping separate “someone knows the password” from “the legitimate account holder is approving this sign-in.” That distinction is especially important for work accounts, where one compromised login may expose customer information, internal documents, or tools used by an entire team.
What I like about this approach is that it does not try to replace the account’s normal sign-in process. Salesforce Authenticator sits beside it. I still begin with the service’s login screen, but the approval on my phone adds another moment where I can recognize or reject the attempt. That makes the app easier to understand than a security product that tries to become a complete password manager, identity platform, or device-management suite.
The app is therefore best judged by how reliably it handles that one job. It is not a general productivity tool, and I would not install it expecting note-taking, password storage, account recovery, or broad device protection. Its value appears when a supported business login asks for confirmation and the phone is available to provide it.
The approval is more meaningful than another password
A second password can still be forgotten, copied, or entered into the wrong place. A phone approval changes the interaction. Instead of relying entirely on something I know, the sign-in also depends on something I have with me. That does not make an account invulnerable, but it raises the difficulty of using a stolen password by itself.
There is also a useful psychological benefit. A sign-in request arriving when I am not trying to access an account is a warning that deserves attention. I can treat an unexpected prompt as a possible sign of a compromised password rather than automatically tapping through it. Never approve a request simply because it appears; the approval should match an action I actually started.
How I use it during a normal sign-in
In everyday use, the flow is fairly direct. I start signing in to the relevant Salesforce-connected service, enter the usual credentials, and then check the phone when the extra verification request appears. I review the request before approving it. If the timing does not make sense, I leave it unapproved and investigate the account rather than treating the notification as an inconvenience.
This is where the app’s design choice becomes clear: it makes the phone a decision point. The security improvement comes not only from having the app installed, but from paying attention to what the request represents. A rushed tap weakens the benefit, while a deliberate approval keeps the second step meaningful.
For a first-time setup, I would do it when I have time to test the complete sign-in flow, not five minutes before an important meeting. Keep the phone charged, make sure notifications are visible, and sign out and back in while the old method is still available. That simple preparation can prevent the unpleasant situation of discovering a verification problem when access is urgently needed.
What happens when the phone is inconvenient
The biggest practical question is whether the extra step becomes annoying. My answer is: it depends on how often I sign in and how dependable my phone routine is. If I normally carry the phone, keep notifications under control, and use the same business accounts throughout the day, the interruption is small. If I frequently work with a dead battery, switch devices, or keep the phone away from my desk, the same protection can feel like friction.
I would also avoid treating the app as a complete answer to account recovery. A verification app helps during ordinary sign-in, but users should still understand how their organization handles lost phones, replacement devices, and locked accounts. Those situations are not reasons to avoid two-step verification; they are reasons to prepare before an emergency.
A realistic workday with Salesforce Authenticator
Imagine I am working from a coffee shop and need to open a Salesforce account to check a customer record before a call. I enter my password on the laptop, then look at the phone rather than clicking blindly on the computer. The request arrives while I am expecting it, so I approve it and continue. Later, while I am away from the laptop, an unexpected request appears. I reject it because I did not initiate a login.
That second moment is the part many basic sign-in explanations overlook. The app is not merely a button that lets me proceed. It can also make suspicious activity visible at the moment it happens. The usefulness depends on my behavior, but the workflow gives me a clear opportunity to notice something wrong.
For a small business owner, this can be more valuable than it first appears. Owners often reuse accounts across a busy day, move between office and home, and work on unfamiliar networks. A second check does not remove every risk, but it reduces the damage of a password being exposed through an unrelated website or a deceptive message.
For an employee, the benefit may be even more concrete: the organization can require an additional check without asking every person to memorize another complicated secret. The trade-off is that the employee must treat the phone as part of the work login routine. That is manageable for most desk-based roles, but less convenient for people who work in areas where phones are restricted, stored away, or difficult to access.
Small habits that make the protection stronger
My first tip is to pause before every approval and compare it with what I just did. A request that arrives seconds after I began signing in is different from one that appears while I am reading email or walking away from the computer. This habit is more important than speed.
My second tip is to test the process from the places where I genuinely work. A login that succeeds at home may feel different in an office, on a trip, or during a remote-work session. Testing early helps reveal whether the phone is easy to reach and whether the notification is noticeable without making it so intrusive that I dismiss it automatically.
My third tip is to plan for device changes before they happen. Replacing a phone is routine, but losing access during a workday is not. I would check the organization’s sign-in and recovery procedure while I still have access, and I would not erase the old device until the new arrangement has been confirmed. The app can be simple to use and still require sensible account planning around it.
A fourth useful habit is separating approval from multitasking. If I am driving, presenting, or handling confidential material, I should not approve a request just to clear a notification. Waiting until I can verify the action is a small cost compared with authorizing a login I did not intend.
Where it compares well with familiar alternatives
The usual alternatives in this category include text-message codes, email codes, hardware security keys, and other authenticator apps that generate temporary codes. Each has a different balance of convenience and independence from the phone’s notification flow.
Compared with a text message, an approval-based experience can feel cleaner because I do not have to read and retype a code. It also avoids making the code itself the center of the process. However, anyone who prefers a visible number they can manually enter may find a code-based method easier to understand or more flexible across services.
Compared with a hardware key, the phone is usually easier to carry because it is already part of daily life. A dedicated key can be a better fit for people who want a separate physical device or who work under strict phone restrictions. The phone-based approach is more convenient until the phone is unavailable, misplaced, out of power, or replaced.
Compared with a general authenticator app, Salesforce Authenticator makes the most sense when the accounts I use are part of the Salesforce environment and the organization expects this particular approval workflow. A broader authenticator may be more suitable for someone managing many unrelated services from different providers. I would not choose this app solely because I want one universal tool for every login.
The friction I would not ignore
The first limitation is dependence on the phone. The extra verification step is helpful precisely because the phone is separate from the computer, but that separation can become a problem when the phone is unavailable. A forgotten phone, a depleted battery, or a notification missed among many alerts can delay access.
The second limitation is attention. An approval prompt is only protective if I distinguish expected requests from unexpected ones. In a busy workplace, repeated prompts may encourage careless tapping. I would rather accept a brief pause than train myself to approve automatically, but organizations should still make the login process clear enough that employees understand what they are confirming.
The third limitation is scope. This is a business security app, not a replacement for strong passwords, careful phishing awareness, device updates, or sensible account administration. It adds a valuable barrier, but it cannot decide whether a message is fraudulent, repair a compromised device, or recover every account problem on its own.
There is also a human trade-off in shared work. If a team depends on one person’s phone for an account, that arrangement can create avoidable delays when the person is on leave or changes roles. I would prefer each user to have an appropriate individual sign-in and a clearly understood recovery path rather than turning one phone into a permanent bottleneck.
Who gets the most from it
I think Salesforce Authenticator is a strong fit for people who regularly access Salesforce-related business accounts, carry their phone during work, and want a second check that is easier than typing a code every time. It is particularly sensible for remote workers, managers who approve access while moving between locations, and small teams trying to improve login security without adding a separate physical token.
It can also suit users who are already comfortable with phone notifications and who will take unexpected requests seriously. The app rewards a calm, deliberate routine. Someone who checks the request before approving gains more from it than someone who treats every prompt as an obstacle.
I would be more cautious about recommending it to a person looking for a universal authenticator for dozens of unrelated accounts. I would also hesitate for anyone whose work rules prevent regular phone access or whose organization has not explained device replacement and recovery. In those cases, a different verification method may fit the working environment better.
The app is free, carries an Everyone age rating, and its long availability makes it approachable for a wide range of business users. Still, the absence of a purchase price does not remove the operational cost of training, recovery planning, and employee habits. The real question is whether the added check fits the way the account is used.
My recommendation after using the workflow
I see Salesforce Authenticator as a focused security layer rather than an all-purpose app. Its strongest effect is simple: a stolen password is no longer the entire key to the account, and an unexpected login can become visible on the phone. That is a meaningful improvement when the approval is deliberate.
My recommendation is positive for Salesforce users who want a straightforward second step and can keep their phone available. I would set it up during a quiet moment, test the complete sign-in process, and learn the recovery procedure before relying on it for important work. I would also explain to every user that rejecting an unfamiliar request is just as important as approving a legitimate one.
In the end, I would choose it for a business account when convenience, phone availability, and Salesforce compatibility line up. I would choose another option when I need one authenticator for many unrelated services, a method independent of a smartphone, or a physical key designed for stricter security routines. For the right situation, though, Salesforce Authenticator turns two-step verification into a practical habit instead of a complicated extra task.
Gallery
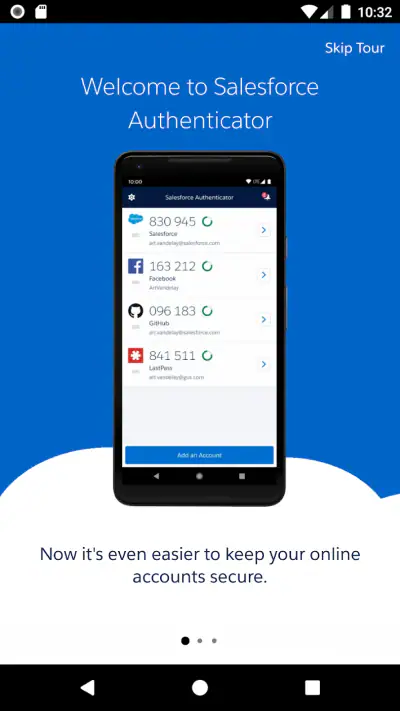
Salesforce Authenticator Pros and Cons
- One-tap push approvals make sign-ins quick and convenient.
- Supports biometric unlocking for an extra layer of protection.
- Works with multiple Salesforce accounts and connected services.
- Provides temporary verification codes when push notifications fail.
- Device registration helps administrators enforce trusted access policies.
- Requires access to the registered phone for most login approvals.
- Push notifications may be delayed by battery or network restrictions.
- Switching to a new phone can require account recovery steps.
- Some advanced security settings depend on Salesforce administrator policies.
- The app offers limited value outside services configured for Salesforce authentication.
Salesforce Authenticator Frequently Asked Questions
What is Salesforce Authenticator and what is it used for?
Salesforce Authenticator is a mobile security app that adds two-factor authentication to Salesforce accounts and supported services. After linking it to your account, the app can send a push notification when a login requires approval. You review the login details, such as the device or approximate location, and approve or deny access directly from your Android or iOS phone.
How do I set up Salesforce Authenticator for my account?
To set up Salesforce Authenticator, install the official app on your phone and open the security or verification settings in your Salesforce account. Choose the option to connect an authenticator app, then scan the displayed QR code or enter the provided phrase in the mobile app. Follow the prompts until the account is successfully linked and tested.
Does Salesforce Authenticator work without an internet connection?
The app generally needs an internet connection to receive push notifications and communicate with Salesforce during a login attempt. In some configurations, Salesforce Authenticator can generate a temporary verification code that may be useful when push approval is unavailable, but availability can depend on the organization’s security settings. Keep your phone connected whenever possible.
What happens if I lose my phone or get a new device?
If your phone is lost, stolen, replaced, or reset, you should contact your Salesforce administrator or use another configured verification method to remove the old authenticator connection. Then install Salesforce Authenticator on the new device and complete the pairing process again. Keeping backup verification options enabled is strongly recommended to avoid being locked out.
Is Salesforce Authenticator safe, and what permissions does it require?
Salesforce Authenticator is designed to strengthen account security by requiring an additional approval beyond your password. It may request permission for notifications so it can alert you about login attempts, while location-related features can help display contextual information for verification. Review every login carefully and deny unexpected requests, since approving an unfamiliar sign-in could allow unauthorized access.














